


AI Agent Governance:
A CISO’s 2026 Checklist
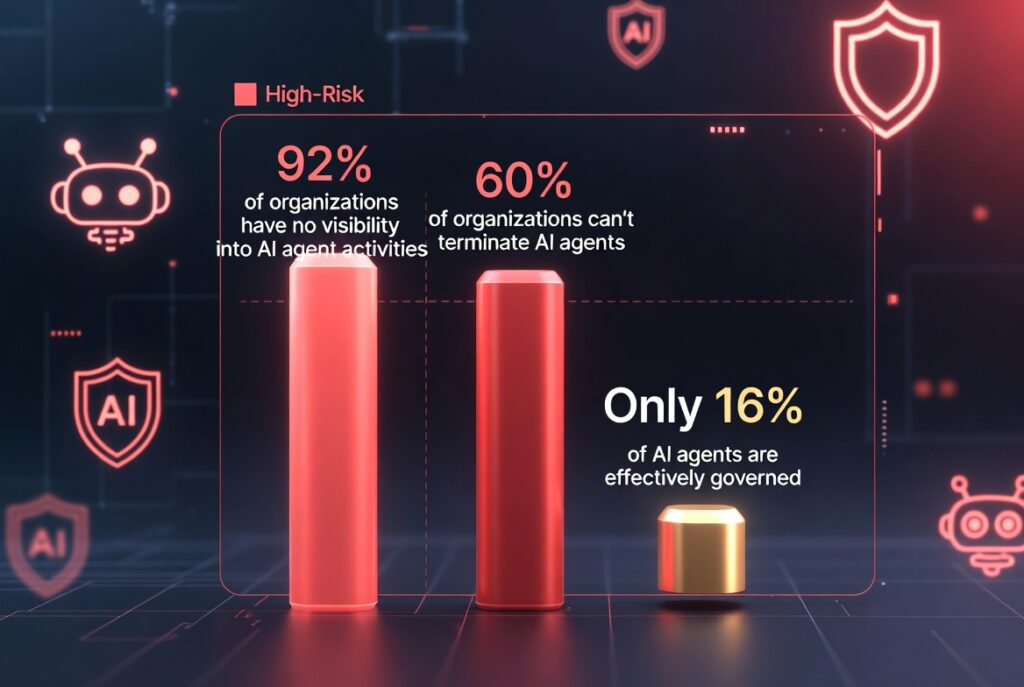
Your agents are already in production. They’re touching your ERP, your CRM, your cloud configs — and 92% of security leaders can’t see them clearly. This is the operational framework that closes the gap.
- Gartner projects 40% of enterprise apps will embed AI agents by end of 2026. Your governance posture isn’t ready: only 16% of organizations effectively govern AI access to core business systems.
- At RSA 2026, the most alarming stat on the floor: 60% of CISOs cannot terminate a misbehaving agent once it’s running. 59% admit shadow AI operates entirely outside their governance perimeter.
- The OWASP Agentic Top 10 (December 2025) is now the canonical threat model. All 10 risks live at the execution layer, not the model layer — which is where most governance programs currently focus.
- This checklist is 10 controls. Items 1, 4, and 7 are the ones I’ve watched organizations skip and regret. Start there.
The 2026 Inflection Point — Why This Year Is Different
Three years ago, “AI governance” at most enterprises meant a PDF in a shared drive and a Slack reminder not to paste customer data into ChatGPT. That era is over. Established
Gartner projects that 40% of enterprise applications will embed task-specific AI agents by the end of 2026 — up from fewer than 5% in 2025. These aren’t chatbots. They query live databases, send emails, execute code, and modify cloud configurations, often with the permissions of the human who provisioned them. The blast radius of a governance failure has changed completely.
The Cisco/Splunk CISO Report, surveying 650 global CISOs in mid-2025, found 86% fear agentic AI will expand the social engineering attack surface, and 82% worry about faster adversarial persistence enabled by AI autonomy. Meanwhile, Mandiant’s M-Trends 2026 report (released at RSAC) revealed attacker dwell time has collapsed to 22 seconds — faster than any human-in-the-loop defense can react. Established
The governance gap is structural. The NCCoE’s concept paper published February 5, 2026 on AI agent identity and authorization is just that: a concept paper, not finished guidance. Even the identity-specific problem hasn’t been solved by a completed framework. CISOs are building planes while flying them. Probable
The organizations that most need autonomous defense (because they’re under AI-driven attack) are the same ones that cannot yet govern autonomous systems. You cannot deploy the shield until you can answer: who owns the agent, what can it touch, and who can shut it down in under 60 seconds?
The 10-Point AI Agent Governance Checklist
These controls are sequenced by dependency, not importance. Item 1 is foundational — nothing below it works without it. I’m pulling these from cross-referencing OWASP Agentic Top 10, NIST AI RMF, and what actually surfaced at RSAC 2026. My sample skews large-enterprise B2B; SMB will find items 6 and 9 less immediately applicable.
You cannot govern what you cannot see. Zenity’s governance framework identifies this as the single foundational control: without a reliable inventory, no downstream control is enforceable. Inventory each agent’s purpose, identity inheritance, data access paths, owner, environment, and integration surfaces.
The complication: 59% of organizations admit shadow AI operates entirely outside their governance perimeter. Unsanctioned agents — spun up by a development team without security review — are where the real exposure lives. Shadow AI incidents carry an average additional cost of $670,000 over standard breaches, driven by the time it takes to scope what the agent touched.
Non-human identities now outnumber human identities 100-to-1 in the average enterprise. IDC projects 1.3 billion AI agents in operation by 2028. Your IAM quarterly access reviews cover 1% of your actual identity surface if you haven’t extended to agents. Every major vendor at RSAC 2026 shipped agent identity capabilities: Microsoft’s Entra Agent ID, Okta, SailPoint, Palo Alto Cortex AgentiX. Established
The critical principle: each tool call should re-authenticate against current context, not against a token issued at session start. Zero trust was built for human sessions. Agents persist, reuse tokens, and share credentials across multi-step workflows. That’s a different threat model.
The 2026 CISO AI Risk Report found 71% of organizations have AI systems with access to ERP, CRM, and financial systems, while only 16% govern that access effectively. That’s not a governance gap — it’s a governance void. Agent permissions scoped to minimum required access isn’t just good hygiene; it’s the difference between a contained incident and an enterprise-wide breach.
The OWASP Agentic Top 10 ranks “excessive agency” (ASI01) as the highest-impact risk: agents with more permissions than their task requires. Scoping at the tool-call level — not just at provisioning — is where most programs fall short. Established
This is the one I’ve watched organizations skip and immediately regret. 60% of organizations at RSAC 2026 admitted they cannot terminate a misbehaving agent once it’s running. With Mandiant’s M-Trends 2026 showing attacker dwell time at 22 seconds, the inability to instantly revoke an agent isn’t a governance gap — it’s a liability. Established
The question every CISO should answer right now: if an agent starts exfiltrating data at 2 AM, what’s your revocation path, who has authority to execute it, and what’s the documented SLA? If you can’t answer that in under 30 seconds, your answer is effectively “I don’t have one.”
Published December 10, 2025, the OWASP Agentic Top 10 is the most operationally actionable agent-specific security framework currently available. Microsoft open-sourced its Agent Governance Toolkit on April 2, 2026, mapped directly to the same 10 risks. Palo Alto rebuilt Prisma AIRS around the framework. The vocabulary is now standardized. Established
The four risks that deserve immediate attention: ASI01 (Excessive Agency), ASI02 (Prompt Injection), ASI03 (Agentic Supply Chain), and ASI10 (Rogue Agents / Shadow AI). All four live at the execution layer — not the model layer. If your AI governance roadmap starts and ends with prompt filtering, you’ve built a wall in front of a door nobody is using.
The Cloud Security Alliance’s April 2026 research note recommends extending existing SIEM and UEBA architectures to capture AI agent interactions: tool call sequences, external API requests, and data access patterns. The principle is pragmatic: even imperfect coverage is substantially better than none. Anomalous behavior detected after the fact is recoverable; behavior that leaves no log is not. Probable
Agent-to-agent communication is the specific blind spot vendors haven’t solved. VentureBeat’s analysis of five agent identity frameworks at RSAC identified it as one of three gaps none of them solve — alongside self-modification auditing and behavioral monitoring at runtime.
AI agent governance is cross-functional by necessity. CISOs typically sponsor oversight, but operational ownership spans security architecture, legal/compliance, and line-of-business teams. Clear accountability models prevent fragmented supervision — and without them, the same governance gaps get created in three separate departments simultaneously. Probable
The specific failure I’ve seen: M&A activity that introduces unmanaged agents silently. Agents introduced through acquisition can expand operational exposure without review. Your governance committee needs a documented trigger for acquisition due diligence that explicitly includes AI agent inventory and access audit. Who owns that right now? If the answer is “nobody formally,” that’s your answer.
The Model Context Protocol (MCP) has emerged as the de facto protocol controlling how AI agents access tools and data in enterprise environments — and the CISO field is just waking up to its attack surface. The Amazon Q Developer extension incident in July 2025 — where a threat actor submitted a malicious pull request to a public AWS repository to manipulate agent behavior — is now the canonical case study. Established
Prompt injection at the tool layer (not the chat layer) is where real damage happens. The OWASP Agentic Top 10 framework’s ASI02 addresses this specifically. An AI MCP gateway that validates tool calls before execution — similar to a WAF for web apps — is the architectural response. Palo Alto’s Prisma AIRS and several newer entrants (Pragatix among them) have built around this pattern. Probable
The regulatory environment has hardened. EU AI Act enforcement timelines are active. NIST’s AI Risk Management Framework provides the governance backbone, while ISO/IEC 42001 is the certifiable management system for AI security — particularly critical for financial services, healthcare, and government contractors. NIST’s Center for AI Standards and Innovation issued a formal RFI on January 8, 2026 — the first U.S. government step toward agent-specific guidance. Probable
My honest take: ISO 42001’s 12–18 month certification process is genuinely valuable but operationally heavy. The pragmatic path is building capabilities through OWASP and NIST AI RMF first, then mapping to ISO for formal certification. Don’t start with ISO unless an audit deadline forces it.
Agent frameworks have short and unpredictable life cycles — Gartner specifically warns about this. Annual red team exercises made sense when the attack surface changed annually. It doesn’t anymore. Quarterly AI red team exercises specifically designed to test jailbreaking, goal hijacking, and prompt injection against your production agents need to be on the security calendar as a fixed cadence. Probable
The specific threat model to use: MITRE ATLAS for agent-specific adversarial tactics. Data poisoning techniques documented within ATLAS are now surfacing in production environments. Your red team needs the OWASP Agentic Top 10 vocabulary and MITRE ATLAS as their operating framework — not generic penetration test playbooks. Speculative — quarterly cycle standard not yet established industry-wide
The Framework Landscape — What to Use and When
There are more frameworks than any team can implement simultaneously. Here’s how I’d sequence them based on what I’ve seen work in practice — mostly B2B SaaS and financial services environments, so weight accordingly for your sector.
| Framework | Primary Use | Time to First Value | Best For |
|---|---|---|---|
| OWASP Agentic Top 10 | Agent-specific threat model, operational prioritization | Weeks | Security teams; immediate triage |
| NIST AI RMF | Governance backbone; cross-jurisdiction regulatory mapping | 2–3 months | Enterprise-wide AI risk programs |
| MITRE ATLAS | Red team exercises; adversarial AI threat hunting | Weeks (scoped) | Security engineering, red teams |
| ISO/IEC 42001 | Certifiable AIMS; regulatory signaling for customers | 12–18 months | FS, healthcare, gov contractors |
Three Gaps Vendors Won’t Fix for You
VentureBeat’s post-RSAC analysis of five agent identity frameworks — including offerings from Microsoft, Okta, SailPoint, Palo Alto, and CrowdStrike — identified three critical gaps none of them solve. I think this is directionally right. Probable
1. Behavioral monitoring at runtime. Watching what agents actually do — not just what they’re permitted to do — requires continuous observation of tool call sequences and decision patterns. IAM tools weren’t built for this. SIEM was built for logs, not intent inference. The gap is real and current tooling addresses it only partially.
2. Agent-to-agent verification. How does one autonomous agent trust another? In multi-agent pipelines, an orchestrator delegates to sub-agents with implicit trust. That’s a lateral movement vector that traditional network segmentation doesn’t address. No production-ready standard exists for this yet. Speculative — solutions emerging but not mature
3. Self-modification auditing. Detecting when an agent changes its own behavior — through fine-tuning exposure, memory manipulation, or tool-chain substitution — is unsolved. The Amazon Q Developer incident illustrated how subtle this can be.
“The CISOs who get ahead won’t be the ones who deployed the most AI guardrails at the model layer. They’ll be the ones who governed the execution layer first.”
— OWASP Agentic Top 10 analysis, April 2026- The 2026 CISO AI Risk Report (n=235) skews toward large enterprises with mature security programs. Organizations at lower governance maturity will find the sequencing here too advanced — they need items 1, 2, and 4 and nothing else for at least 12 months.
- The OWASP Agentic Top 10 was published in December 2025. It’s authoritative but untested at scale across production environments. Some risk rankings may shift as real-world attack patterns crystallize in 2026 incident reports.
- Vendor claims at RSAC 2026 about “agent identity” solutions should be treated with healthy skepticism. Agent washing — rebranding existing tools as agent-native — is real. Gartner estimates only ~130 of thousands of “agentic AI” vendors are building genuine capabilities.
- The ISO 42001 recommendation reflects compliance-heavy sectors. Most engineering-led organizations will find it premature and operationally distracting before NIST AI RMF controls are actually running in production.
- The quarterly red team cadence (Item 10) is aspirational for most teams. Annual with rigorous scope is more realistic for organizations with under 5 dedicated security engineers. I haven’t tested the quarterly model at scale.
Frequently Asked Questions
- Zenity — AI Agent Governance Checklist for Enterprise CISOs (March 2026)
- Cloud Security Alliance Lab Space — The AI Agent Governance Gap: What CISOs Need Now (April 2026)
- C1 Field CISO Kevin Paige — Top 3 Takeaways from RSA Conference 2026 (April 2026)
- AGAT Software — OWASP Agentic Top 10: CISO Guide (April 2026)
- OWASP LLM AI Cybersecurity & Governance Checklist (2025–2026)
- NIST AI Risk Management Framework (AI RMF 1.0)
- Mandiant M-Trends 2026 Report (RSAC 2026)
- CyberSaint — Top Security, Risk, and AI Governance Frameworks for 2026
- SentinelOne — AI Security Standards: Key Frameworks for 2026 (February 2026)
- Cloud9 — Agentic AI Readiness Checklist 2026
- MITRE ATLAS — Adversarial Threat Landscape for AI Systems
- Model Context Protocol — Official Documentation (Anthropic)
The AI Governance Checklist Companies Are Using to Stay Safe
MCP + A2A Protocol: The Complete Architecture Guide
NotebookLM for Researchers: A Deep Dive Into the Most Underused AI Tool
AI Safety in the Enterprise: What Every CTO Should Know
Agentic Workflows: How AI Systems Are Actually Taking Over Knowledge Work
How to Write a Systematic Review: PRISMA Guide for 2026